European Union
Anti-Corruption Directive
The first harmonised criminal framework across all Member States. Criminalises private-sector bribery and trading in influence. National laws due by 1 June 2028.
Adopted 21 April 2026
Oben Legal PLLC, New York. Attorney advertising.
Anti-bribery and corruption
Washington narrowed its priorities. Brussels, London, Paris and Bern did the opposite. A compliance programme built for the FCPA alone now has structural gaps, not cosmetic ones. This is where those gaps get mapped.
Updated September 2026
The first harmonised criminal framework across all Member States. Criminalises private-sector bribery and trading in influence. National laws due by 1 June 2028.
Adopted 21 April 2026
A documented fraud risk assessment in its own right. The Home Office's own estimate of the work: 100 to 130 hours.
SFO DPA with Ultra, May 2026
Enforcement resumed in June 2025 under narrowed priorities: cartel links, harm to US competitors, national security and serious misconduct.
Guidelines issued 9 June 2025
The SFO, the Parquet National Financier and the Swiss Attorney General, coordinating cross-border bribery investigations directly with one another.
Formed March 2025
The Brief
EU Directive
Four gaps that a US-built compliance programme does not close, and what closing them actually involves.
Third-party risk
Agents, distributors and customs brokers sit behind most bribery cases. Why, and the four controls that actually reduce the risk.
United Kingdom
What a failure-to-prevent-fraud risk assessment has to contain before it counts as reasonable procedures, and why your bribery assessment does not cover it.
Self-disclosure
The DOJ now promises a declination to companies that come forward. The catch is timing, and the number of authorities who may hear first.
A scored self-assessment against the Directive, the UK regime and current DOJ priorities. Fifteen questions, about five minutes, and a result naming your three largest gaps. No email needed until the end.
Practice
Seven engagements and one free tool. Each is scoped to a fixed deliverable, and each says up front which entity delivers it.
The archive
Four years of writing stays online, reorganised around the work: enforcement, integrity programmes, governance, and the technology now sitting inside both.
Charges, settlements and the policy shifts behind them.
How controls, culture and speaking up actually hold together.
Boards, leadership and the decisions that set the tone.
The technology now sitting inside both the risk and the controls.
Who writes this
Attorney at law, New York
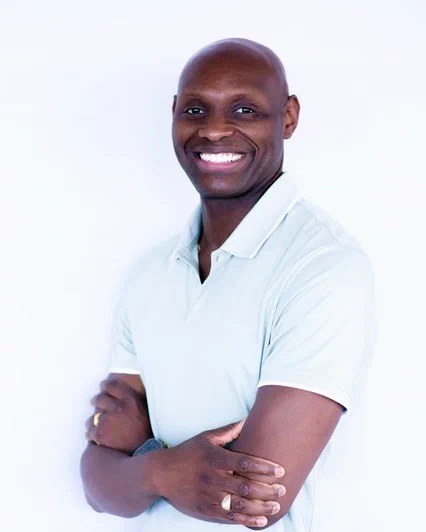
Fifteen years of legal, compliance and enterprise risk work inside institutions that were themselves under scrutiny.
JPMorgan Chase. BNP Paribas. Deutsche Bank. Banco Santander. Ericsson. Building control environments, running investigations, and carrying the consequences of getting either wrong, in organisations where regulators were already in the building.
That is the standard the work here is held to. Mid-market companies now face the same multi-jurisdictional exposure those institutions did, with none of the infrastructure. Closing that distance is the practice.
Programme work is advisory and runs through Themis. Anything that looks backward at conduct already in the past runs through the firm, where privilege attaches.
Themis Advisory Group
Risk assessments, EU Directive and UK readiness reviews, third-party due diligence architecture, training, and fractional chief compliance officer coverage. Fixed fee, scoped up front.
Go to ThemisOben Legal PLLC
Internal investigations, self-disclosure analysis and legal opinions. A gap analysis that surfaces real exposure can be discoverable when a consultancy performs it. Run through counsel, it can be protected.
Request a confidential conversation